

AI, post-quantum cryptography shift signals new era of CLM
Thu, 15th Oct 2026 (Today)
Australian businesses are facing the shift to automated digital certificate management as validity periods shrink and preparations for post-quantum cryptography gather pace.
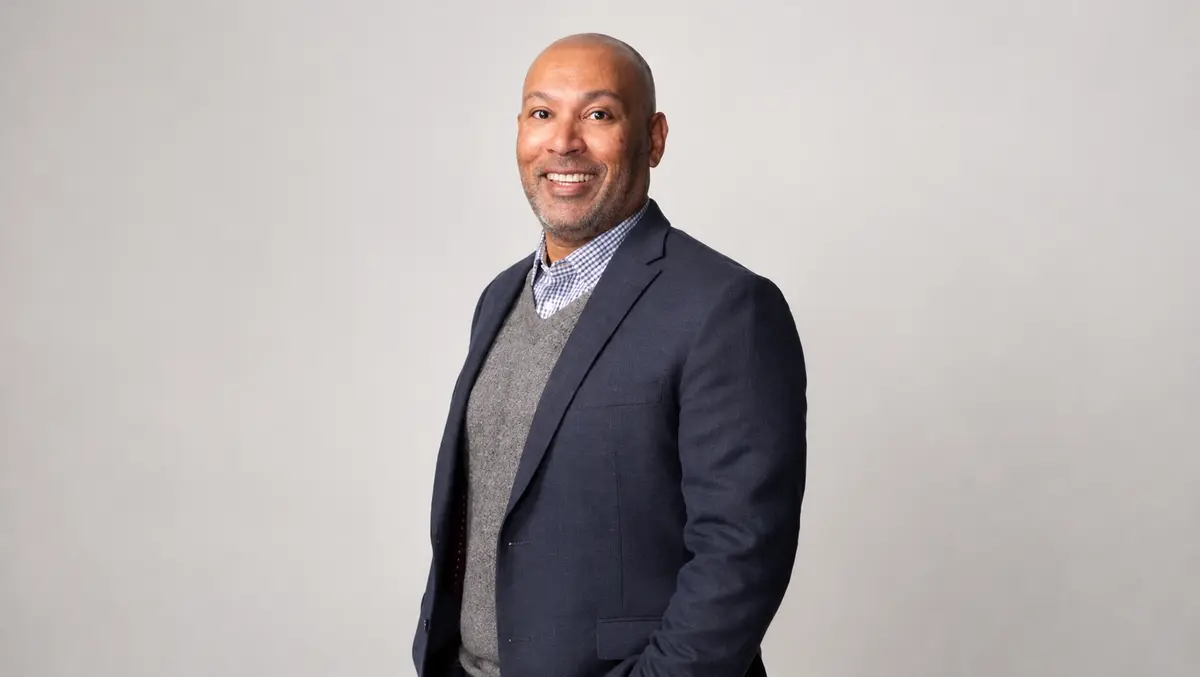
The changes are increasing the frequency with which organisations must renew and replace digital certificates, creating additional administrative demands and potential security risks for businesses that continue to rely on manual processes, said VP of Sales APAC at Sectigo, Ray Garnie.
Garnie said certificate lifecycle management tools are becoming more important as organisations manage more certificates across expanding IT environments, particularly as AI adoption accelerates and the industry prepares for the emergence of quantum computing.
Sectigo, a certificate authority and certificate lifecycle management (CLM) provider, provides tools designed to automatically discover, deploy, renew and revoke certificates across enterprise environments.
The industry is currently undergoing significant change as certificate validity periods shorten, with further reductions expected over the coming years.
"When I started in this industry in the mid-2000s, you could get a certificate that was valid for 10 years," Garnie said.
Since then, validity periods have progressively decreased, moving from 10 years to five years and subsequently to shorter periods.
Under the current schedule, certificates can be valid for up to 200 days, with that period expected to ultimately fall to 47 days by 2029.
The reductions are intended to limit the time compromised or misused certificates can remain trusted, while requiring more frequent validation and allowing the ecosystem to respond more quickly to security changes.
Manual management faces growing costs
The shrinking lifespan of certificates is expected to make manual management increasingly difficult for organisations.
Before automation, companies would track certificate expiry through spreadsheets and rely on employees to monitor renewal dates, issue reminders and replace certificates when required.
These processes created risks when employees left an organisation without properly documenting their work or sharing information about certificates under their management.
This problem is expected to intensify as renewal intervals become shorter.
Under the previous renewal cycle, an employee might have needed to renew a certificate once a year. As validity periods decline, the same certificate could require multiple renewals annually.
"If businesses remain manual, costs are going to go up," Garnie said.
He added that certificate lifecycle management tools could reduce the administrative burden by automating renewals, identifying certificates across an organisation's environment and ensuring they were replaced before expiration.
The tools could also help organisations respond to security incidents by identifying affected certificates and locating the systems where they were deployed.
"Moving into a more utilised CLM and utilising the tools rather than manual process is actually going to save costs, and also ensure that nothing is missed," Garnie said.
Automated discovery and management could therefore help businesses reduce operational costs while limiting the risks associated with expired, overlooked or compromised certificates.
The challenge is particularly relevant as organisations deploy more applications and expand their digital infrastructure, increasing the number of locations where certificates are required.
AI adoption introduces new considerations
Automation is also changing how businesses approach certificate management, with Garnie expecting agentic AI to take on a greater share of routine operational work.
With organisations increasingly implementing AI, that adoption needs to be accompanied by appropriate controls and safeguards.
Sectigo has incorporated AI into its platforms and tools, while enabling customers to integrate AI capabilities into their own environments to help manage certificates.
Garnie described the approach as a collaborative process in which certificate management platforms and customer systems could work together as companies move towards greater automation.
Sectigo expects AI agents to become more involved in handling repetitive tasks, building on the shift away from spreadsheets and manual renewal processes.
However, the broader transition also means businesses must ensure that automated systems operate within appropriate security controls.
For organisations managing certificates across multiple applications, systems and environments, visibility remains an important requirement.
Without a reliable understanding of where certificates are deployed, businesses could struggle to identify affected assets during a security incident or ensure that renewals are completed on time.
Businesses must adapt to post-quantum cryptography
Beyond certificate validity periods, Sectigo has identified post-quantum cryptography (PQC) as the other major development expected to affect the industry over the next several years.
The transition towards cryptographic systems designed to withstand attacks from sufficiently capable quantum computers will require organisations to understand where their existing cryptographic assets are deployed and how they can be replaced.
Garnie said this would make certificate agility - the ability to identify, manage and replace certificates and related assets - more important.
He cited a global study conducted with research organisation Omdia, which found that approximately 90 per cent of organisations saw an overlap between shorter certificate validity periods and preparations for post-quantum cryptography.
"The same visibility and ownership and automation will help enterprises migrate algorithms without major disruptions," he said.
Organisations that already have an accurate inventory of their certificates and automated processes for replacing them are likely to be better positioned to manage cryptographic changes without extensive manual intervention.
Sectigo has established sandbox environments for PQC, allowing customers to trial the technology and assess whether it works within their environments.
The timing and complexity of migration will vary across organisations, but the need to identify existing certificates and understand their deployment is likely to remain a central consideration.
Industry faces era of significant change
Garnie identified shorter certificate lifespans and post-quantum cryptography as the two most significant developments facing the sector, with AI and the growing number of certificate use cases adding to the complexity.
Reduced validity periods are already starting to bring certificate management into sharper focus for organisations, while preparations for PQC become more pressing.
For businesses, the developments point towards a greater need for automated discovery, renewal and replacement processes, alongside the ability to adapt as cryptographic requirements change.
Garnie, who has two decades of experience in the industry, described the current period as the most interesting that he has experienced.
"This is the most exciting time I've been through," he said. "Lots of change, lots of developments happening day after day."
As certificate validity periods continue to decline and post-quantum preparations advance, organisations will need to understand where their certificates are deployed and how quickly they can update them.