Security Keys stories
AI-generated phishing is making employee vigilance less reliable, pushing organisations towards passkeys and phishing-resistant multi-factor authentication.
Australian firms remain exposed as 43% reported AI-driven phishing attacks in the past year, while many staff still log in with passwords.
More than 12,000 inboxes were exposed as the kit used to bypass multi-factor authentication and sustain account access was taken offline.
Mortgage brokers face mounting breach and fraud risks as attackers exploit SMS codes to reach high-value client data, experts warn.
Fraudsters are exploiting tax season by stealing credentials and filing bogus returns, putting Australian refunds and ATO accounts at risk.
Stolen credentials are fuelling fraud as attackers bypass ATO controls, exposing taxpayers and forcing tax agents to harden logins.
Security teams may miss the attack because it leaves no persistent phishing site, instead building fake Microsoft login pages inside the browser.
Australian users of OpenAI's security programme will now need hardware-backed passkeys, as older sign-in methods are disabled for higher-risk accounts.
Approved defenders will gain broader access to cyber tools as the new tiered Daybreak programme adds GPT-5.6-Cyber for advanced security work.
Google says the campaign is shifting towards financial and legal firms, with rebranded extortion sites still stealing cloud logins and tokens.
Phishing-resistant logins could curb account takeovers that let criminals tamper with tax data, refunds and audit trails across firms.
Automated requests now make up most web traffic, raising costs for sites and sharpening fears over AI-driven fraud and phishing.
Victims can be tricked more easily as Logokit now tailors fake login pages in real time, sending stolen credentials to Telegram bots.
Users relying on SMS or voice for sign-ins will be nudged to passkeys as Microsoft phases out weaker multifactor methods in Entra ID.
Users who miss the deadline will lose access to OpenAI's most advanced cyber models, as the firm tightens defences against phishing.
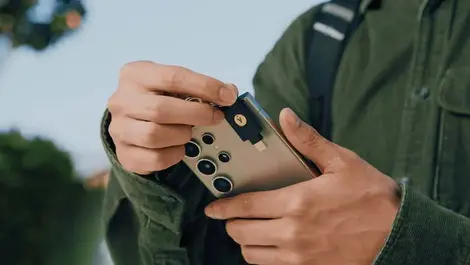
Android users and IT teams can now deploy YubiKeys as hardware-backed passkeys, following Google Play Services support for NFC security keys.
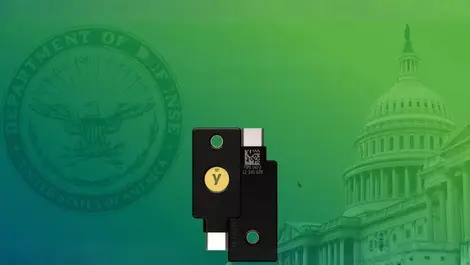
The upgrade gives government and regulated buyers a single device for legacy smart cards and passkeys, as agencies shift to stricter security rules.
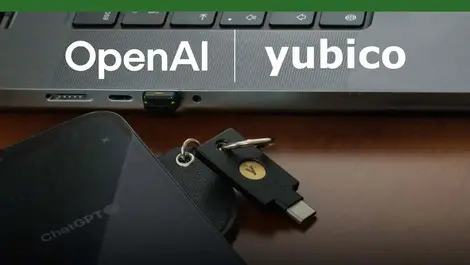
ChatGPT users can now buy a discounted two-pack of hardware keys designed to block phishing and protect sensitive accounts.
Reporters face rising risks from phishing, spyware and device compromise as Bitdefender urges tighter source protection and account security.
Despite leading on passkeys and MFA, Indian firms still face widespread AI phishing and deepfake scams that are undermining daily security practice.