AI Safety stories
The incident has sharpened calls for tighter controls as automated systems grow better at probing weaknesses across public and private networks.
Growing use of AI agents in corporate systems is creating a new internal risk category, prompting tighter real-time oversight from security teams.
Security teams facing new risks from generative AI can now take eight hours of hands-on training on prompt injection and jailbreaks.
The deal should help large firms deploy safer AI systems, with HCLTech adding Claude to services and software for banks, hospitals and manufacturers.
Autonomous systems are exposing governance gaps, leaving companies scrambling to monitor access, review decisions and curb machine-speed attacks.
Canadian law firms can keep client files walled off, while choosing data storage and processing become key topic for AI in law.
The tool aims to help engineers catch unsafe or inaccurate AI outputs before they reach customers, as firms push generative systems into production.
Publicly boasting about AI security breaches could soon hand regulators and litigants a ready-made paper trail.
Customers can now run AI agents with built-in memory and governance as MongoDB tries to move them from pilots into daily use.
The new service lets users delegate ongoing work to persistent agents that can act across apps, raising fresh privacy and control questions.
Attendees will see connectivity pushed into new sectors as dedicated automotive, health and aviation zones join the Barcelona show in 2027.
As AI budgets rise to USD $210 million, firms are tightening oversight on security, governance and returns to keep deployments under control.
The appointment comes as firms race to secure autonomous AI agents that can access systems and physical infrastructure without human oversight.
Encrypted data exchanges in smart transport can now run far faster on Intel chips, easing a key barrier to edge AI deployment.
Public bodies could cut admin and free staff for frontline cases if ministers back AI tools with stronger oversight and safeguards.
The package will support UK research into agentic safety and security as autonomous AI systems spread, with startups also receiving backing.
Rising concern over AI oversight is pushing firms to audit overlooked systems that may still hold access to sensitive company data.
The new tool aims to curb agent failures and costly manual fixes as 79% of enterprises report reversing AI actions in Kore.ai's survey.
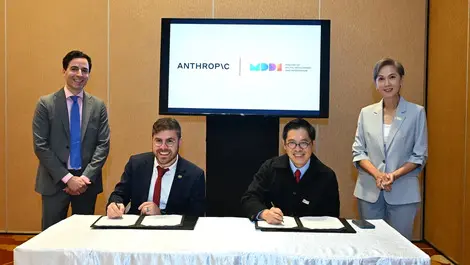
The deal expands Anthropic's Asia-Pacific footprint and gives Singapore closer access to its AI safety and model-testing expertise.
Smaller specialist models could save UK banks millions on compliance work while reducing reliance on a handful of US tech giants.